THIS WEEK GoTo.now vs. TinyURL: An In-Depth URL Shortener Showdown Read this week's article →

Organize team access with workspaces and security policies

Create a shared boundary for members and selected campaigns, assign clear roles, then add OIDC, SCIM, MFA, session, network, retention, and audit controls when needed.

Create a workspace All features
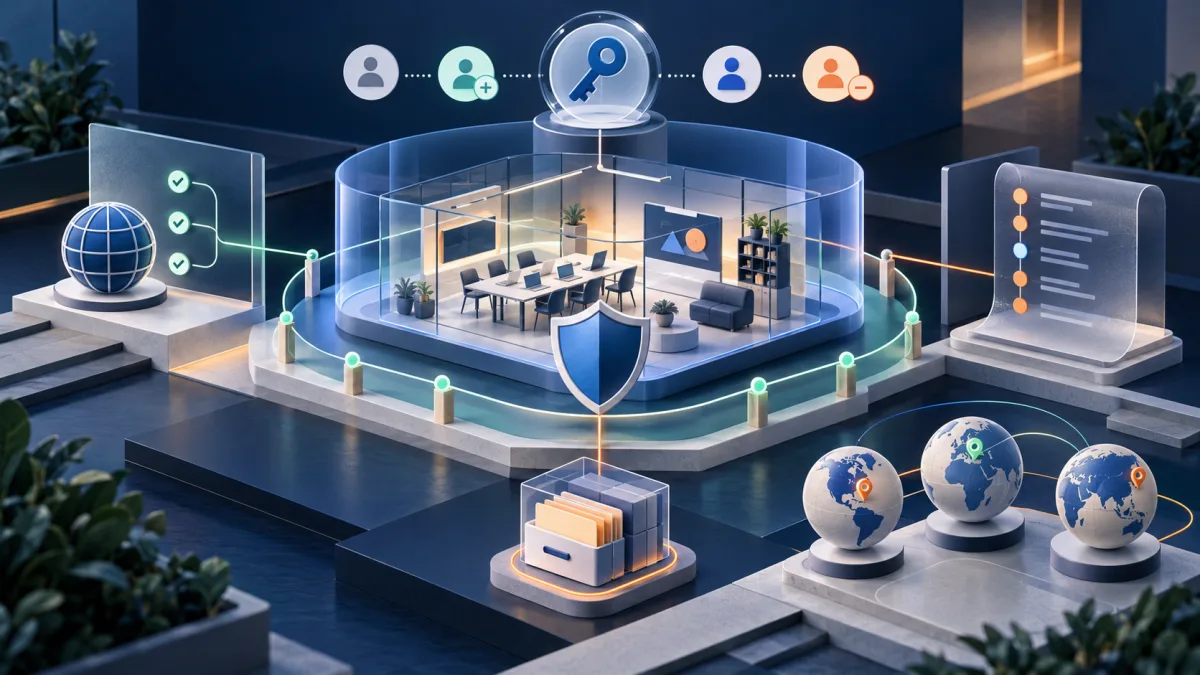
Illustration of a protected team workspace surrounded by identity, lifecycle, network, audit, retention, and regional policy controls

What you can do

Each capability below is available in the current GoTo.now application.

Members, roles, and selected campaigns

A workspace groups invited members with only the campaigns deliberately attached to it. Owners and admins manage membership; editors work on shared campaigns; viewers receive read-only access.

OpenID Connect SSO

Connect an OIDC discovery issuer, client ID, and encrypted secret, then test the workspace-specific sign-in path before enforcement.

SCIM user lifecycle

Generate a one-time bearer token for standards-based user listing, provisioning, role updates, and deprovisioning.

MFA and session enforcement

Require an MFA authentication-method claim from the identity provider and limit enterprise session duration from 15 minutes to seven days.

IP allowlists

Restrict enterprise sign-in and active enterprise sessions to approved addresses or CIDR networks.

Retention controls

Apply the shortest owner workspace policy to old audit, completed job, and privacy-safe clickstream records in the scheduled worker.

Audit export

Download up to 50,000 recent account actions as CSV for review or external archiving.

Onboard an agency team without sharing a company password

A workspace owner connects an OIDC issuer, tests sign-in, provisions members through SCIM, requires an MFA claim, limits sessions to eight hours, and restricts access to office and VPN networks. A departing contractor is deactivated through the same lifecycle endpoint.

What this changes: Identity and access changes remain scoped to the workspace, while material actions are available in the audit export.

Is this the right tool?

Use it when

  • Several people need role-based access to selected campaigns
  • A managed identity provider should control workspace access
  • Joiner, mover, and leaver changes need an API lifecycle
  • Network, session, retention, or audit policy must be explicit

Choose another approach when

  • One person owns and manages every link
  • You require SAML rather than the live OIDC flow
  • A region preference alone must guarantee physical migration
  • You need an SLA before commercial operations can support it

How it works

1

Create the team boundary

Name the workspace, invite members as admin, editor, or viewer, and attach only the campaigns they should share.

2

Work together with clear ownership

The workspace owner keeps control while members use their own accounts instead of sharing a password.

3

Add security policy when needed

Configure OIDC, SCIM, MFA, session, network, retention, and regional preferences, then review the activity export.

Create a workspace

Behavior worth knowing

  • OIDC is the live SSO protocol. SAML is not advertised as active without a configured SAML service provider and certificate workflow.
  • A data-region selection records the required deployment preference; physical residency depends on the contracted hosting region.
  • An SLA is a commercial operating commitment, not a dashboard toggle; service status remains publicly visible.

Workspaces & Enterprise Security FAQs

What is a GoTo.now workspace?
A workspace is a team access boundary. It connects invited members to selected shared campaigns with explicit roles. It does not automatically expose the owner's personal link library or unrelated campaigns.
What can each workspace role do?
Owners control the workspace. Admins can manage members and attach campaigns. Editors can work on shared campaign content. Viewers receive read-only access.
Can I test SSO before enforcing it?
Yes. Save a complete OIDC connection, use Test OIDC sign-in, verify claims and membership, and only then enable enforcement.
What does SCIM support?
The workspace endpoint supports listing, provisioning, role updates, activation state, and deprovisioning with a hashed bearer token.
Does selecting a region move existing data immediately?
No. It records the workspace requirement. Physical migration or dedicated regional hosting must be completed as part of the hosting agreement.

Explore the complete platform

See how link management, routing, analytics, QR, branded domains, automation, and workspace controls fit together.

View all features